
CVE-2024-26152 Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Attackers can inject malicious scripts via uploaded data in Label Studio, potentially stealing cookies or executing code in victim browsers.
- Exploited in the wild
- Not known
- Login needed
- Not needed
- Attackable
- Over the internet
- Victim action needed
- A user has to click or open something
- Fix
- Available
What is CVE-2024-26152?
CVE-2024-26152 is a medium-severity cross-site scripting vulnerability in HumanSignal label-studio, published on 22 Feb 2024. An attacker can exploit it over the internet without logging in, and only if a user opens a file or follows a link.
Official description
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project. 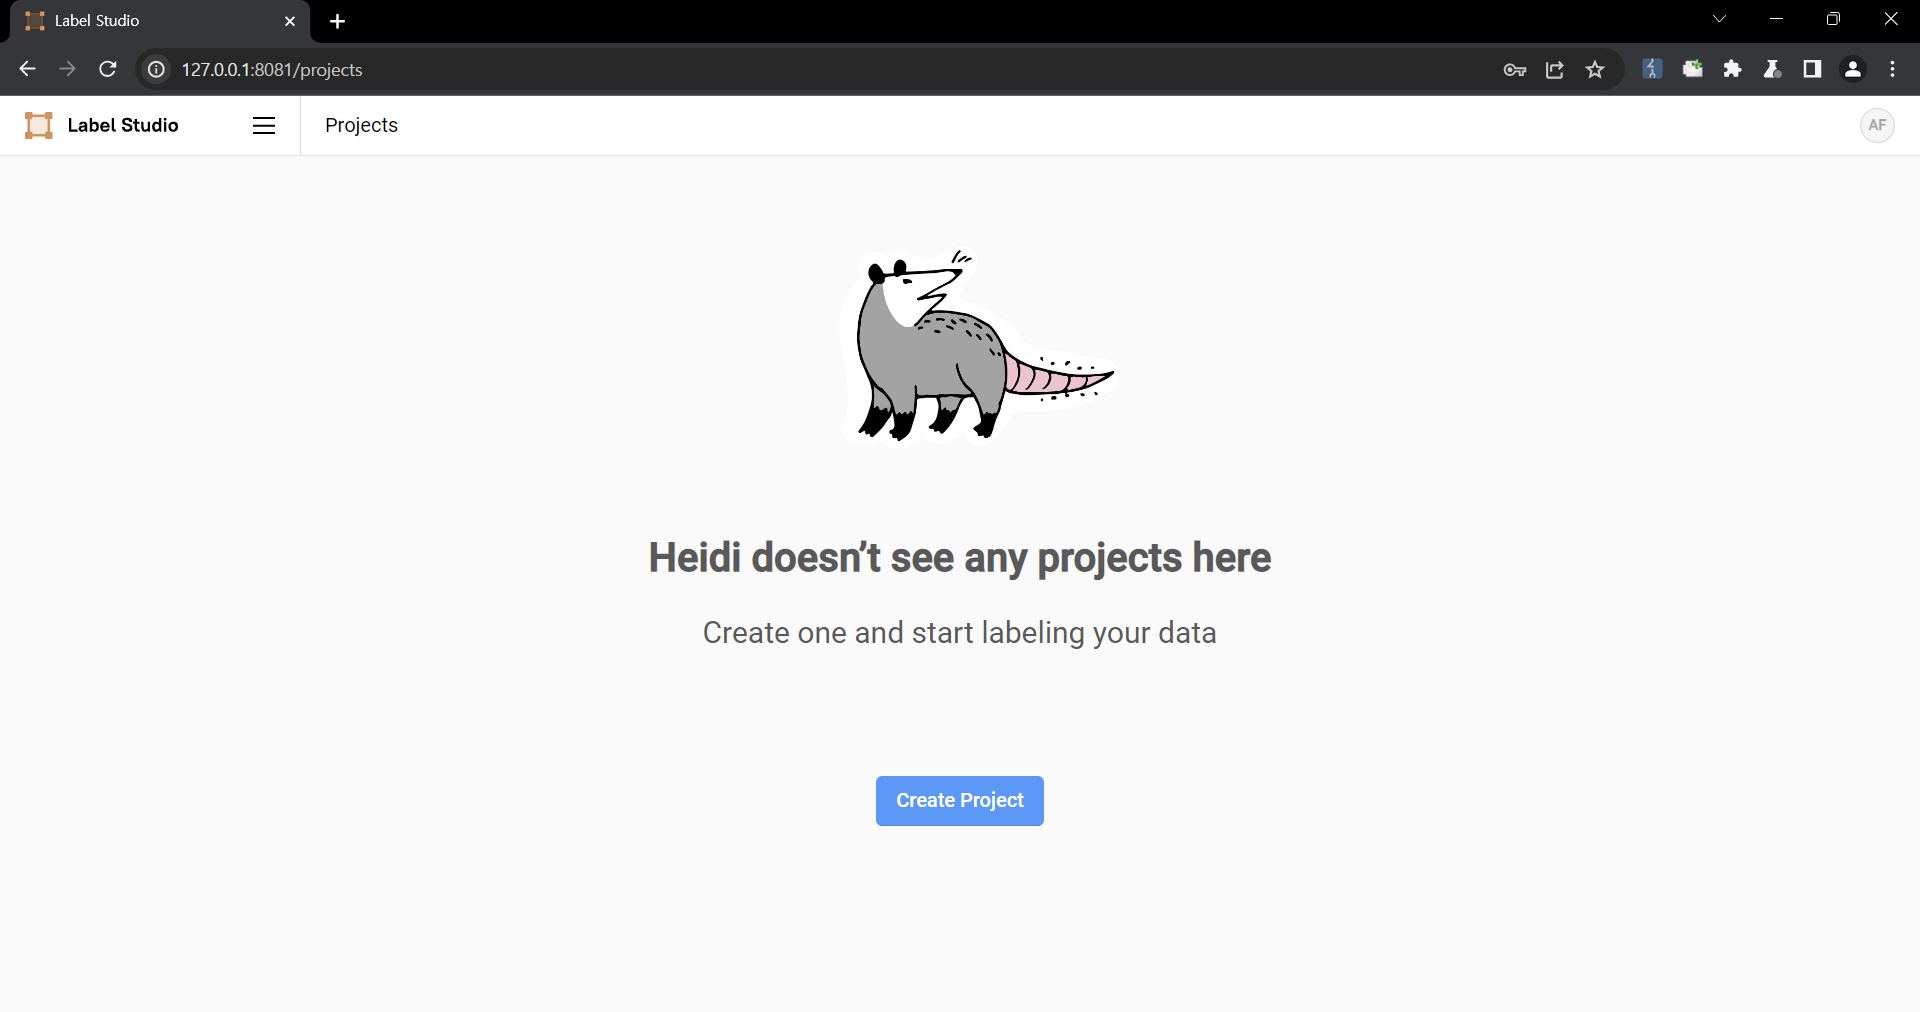
2. Upload a file containing the payload using the "Upload Files" function. 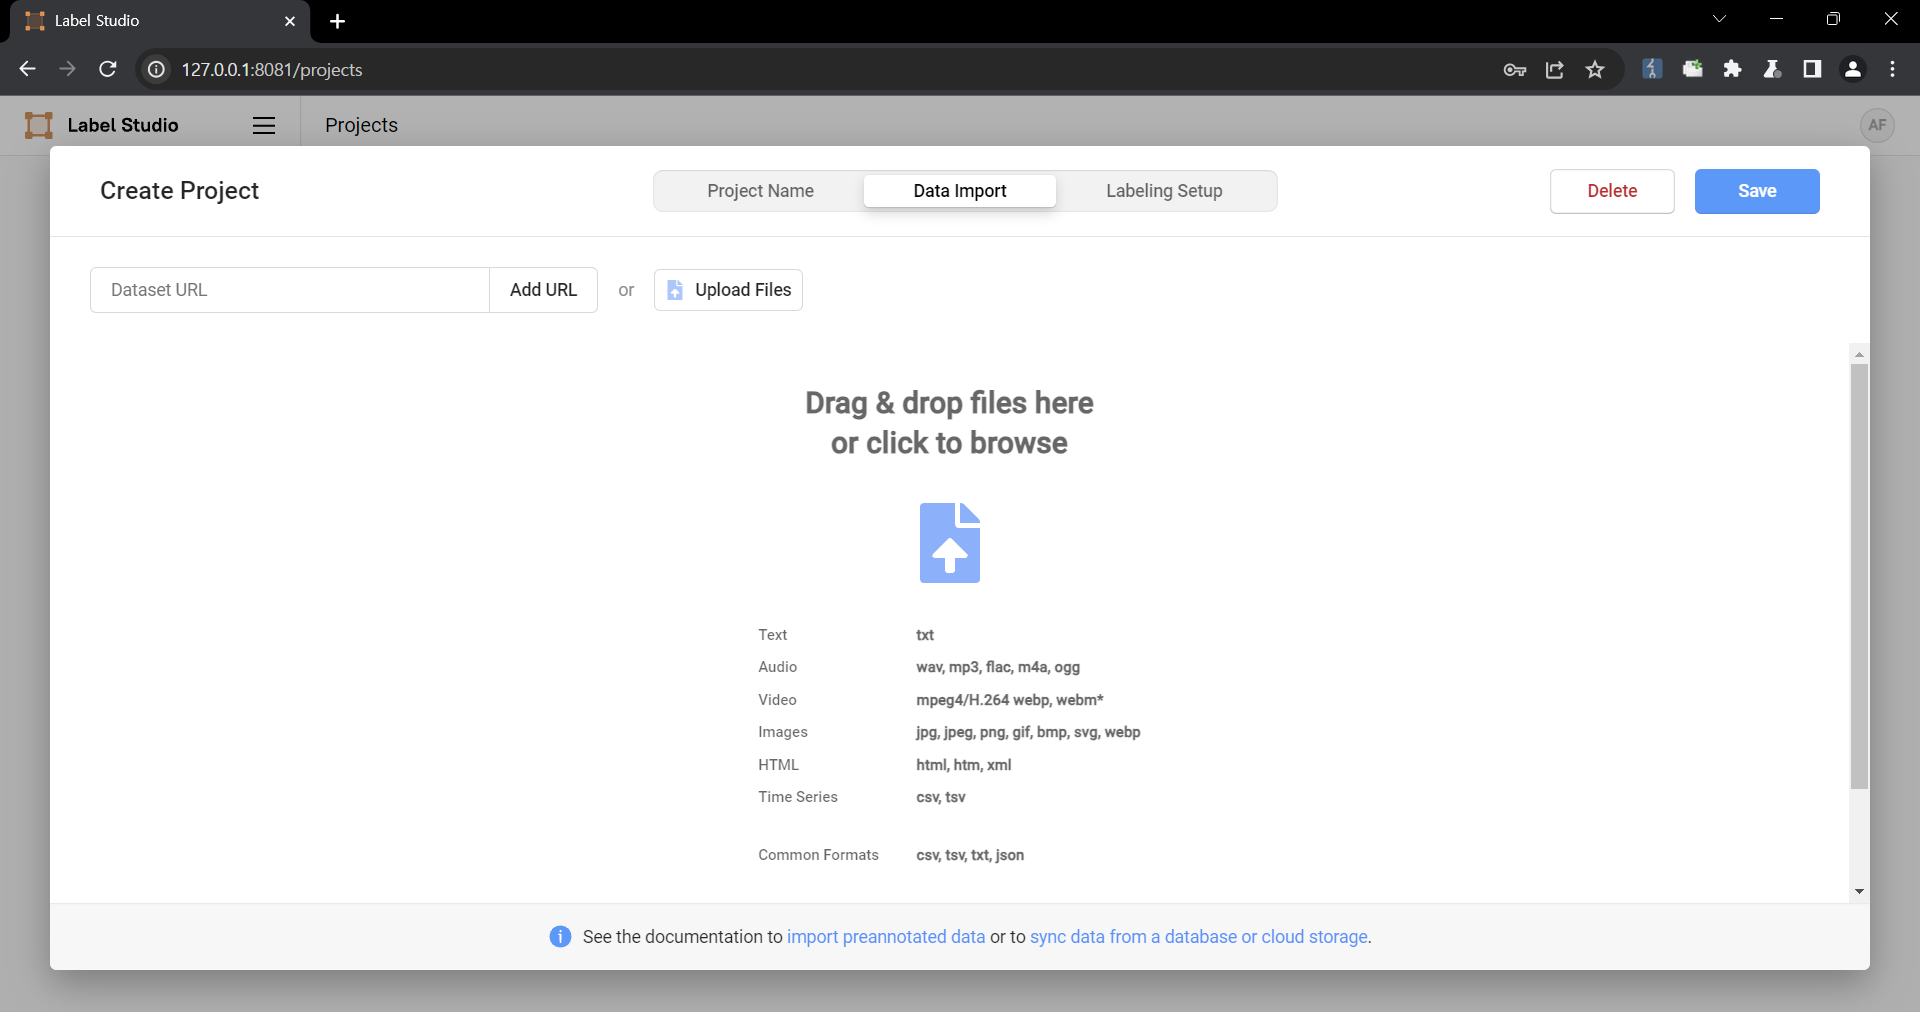 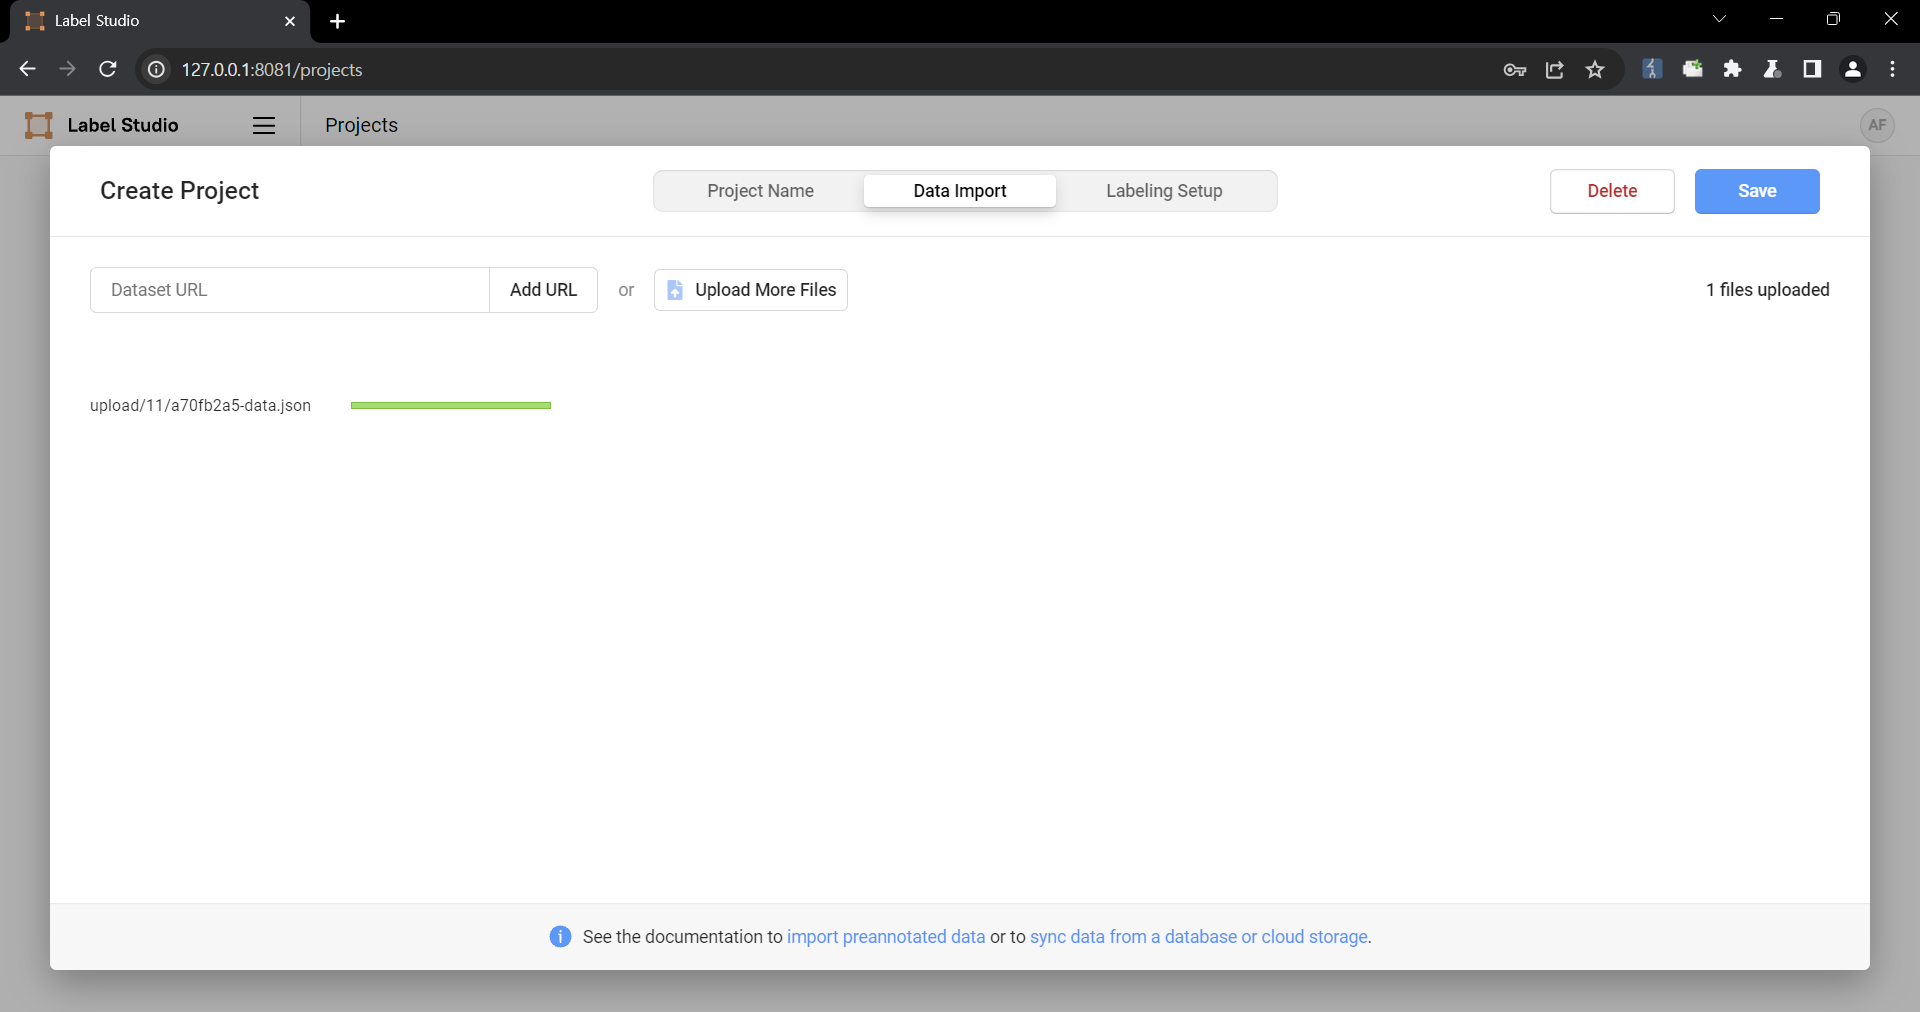
The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ```
3. Select the text-to-image generation labeling template of Ranking and scoring 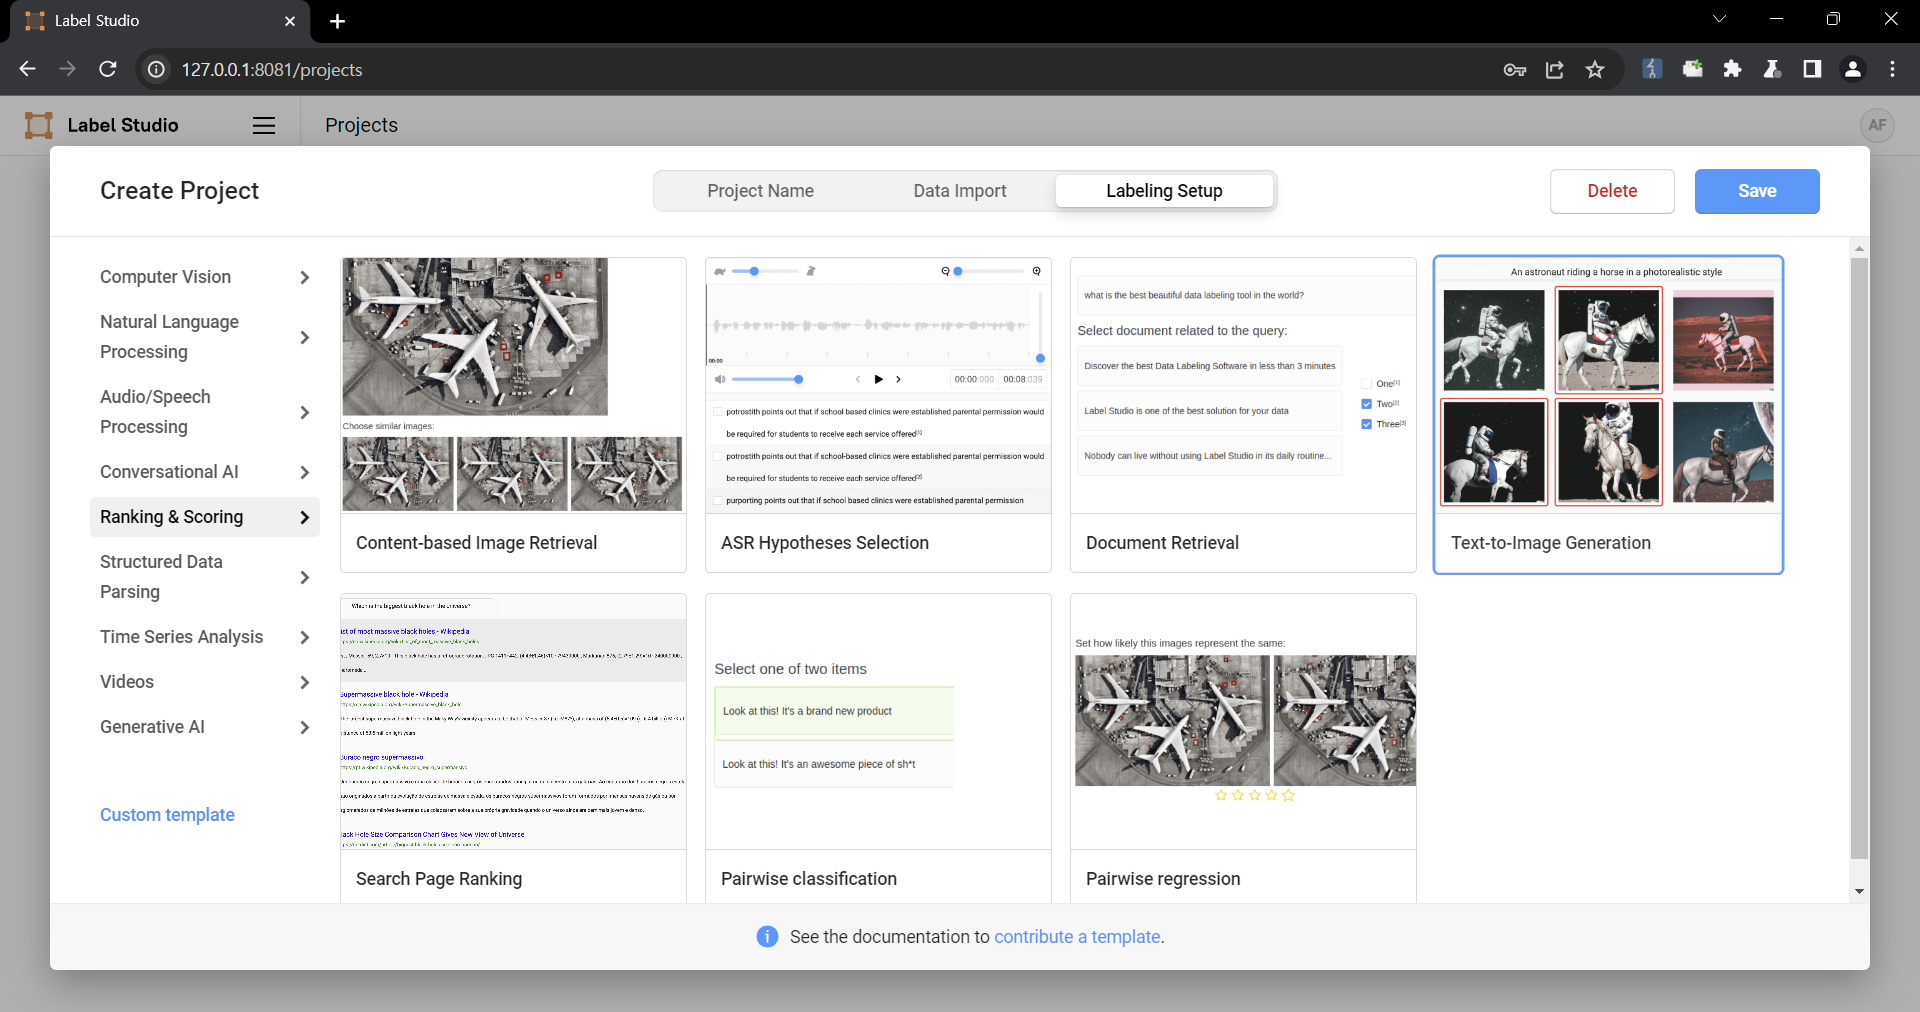 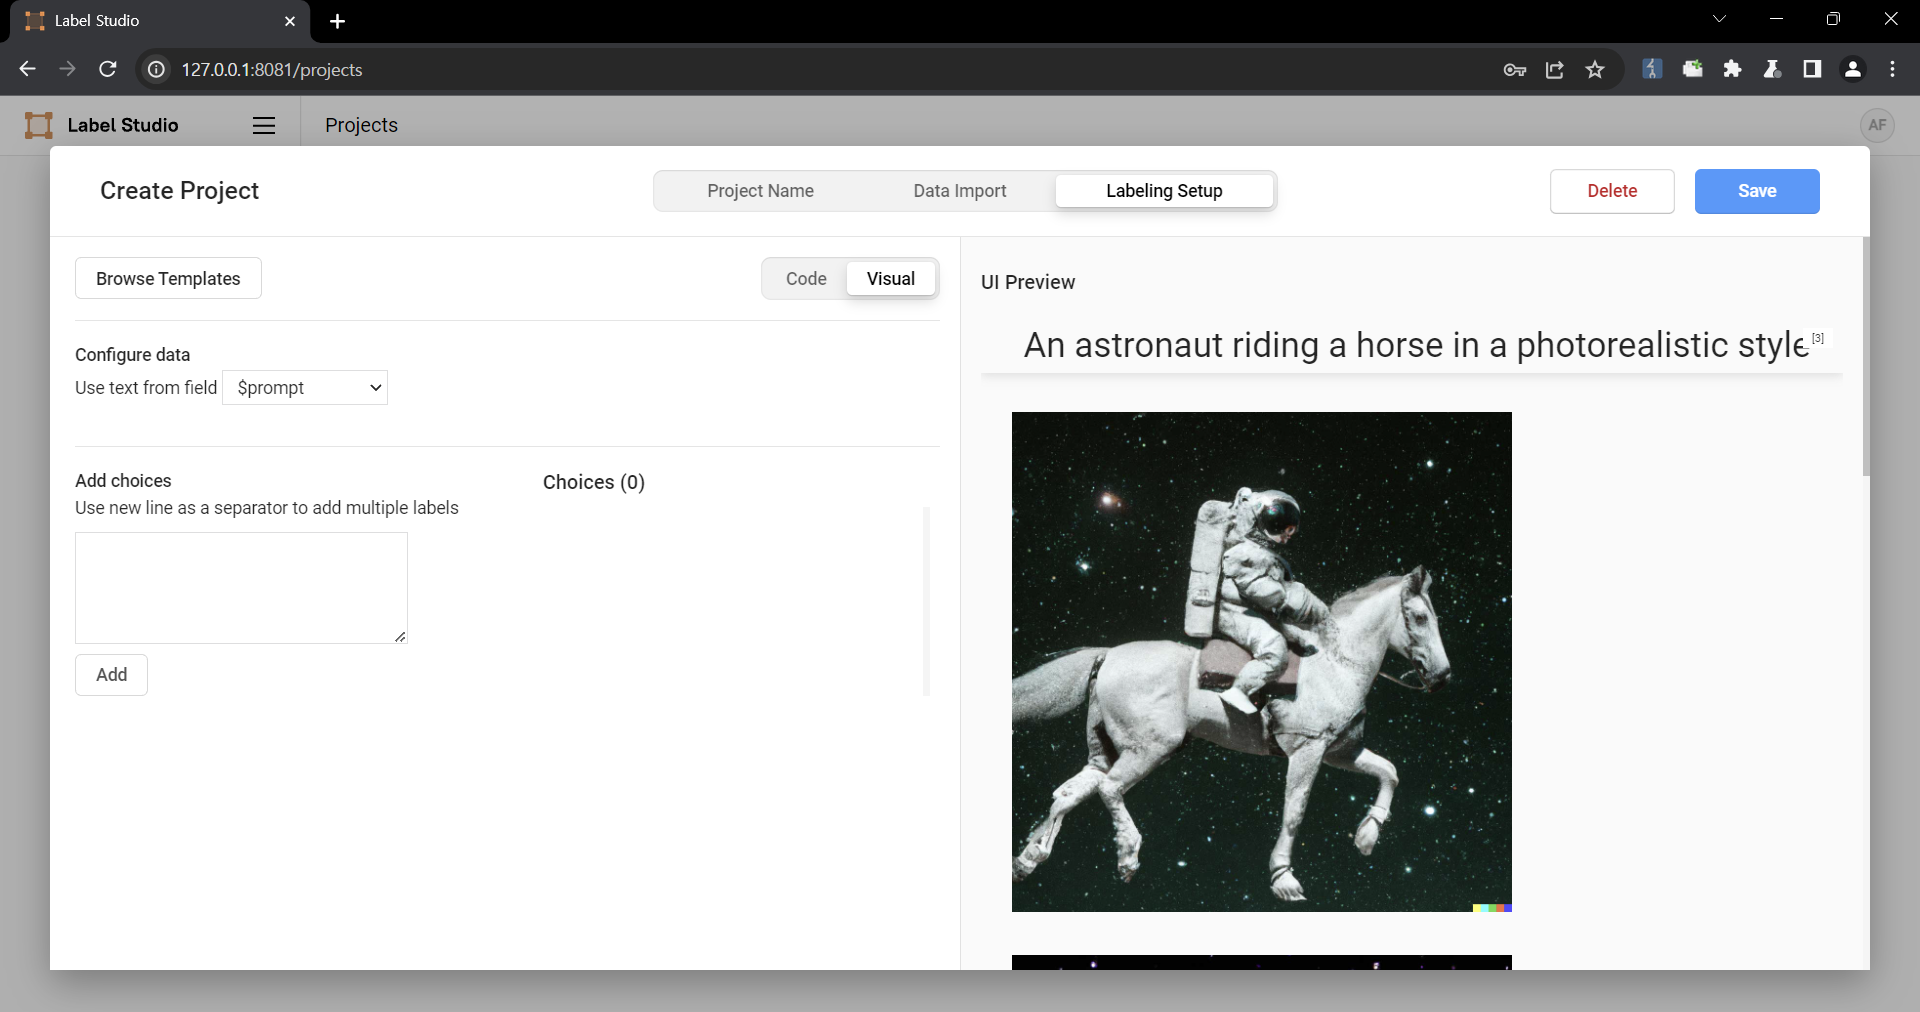
4. Select a task 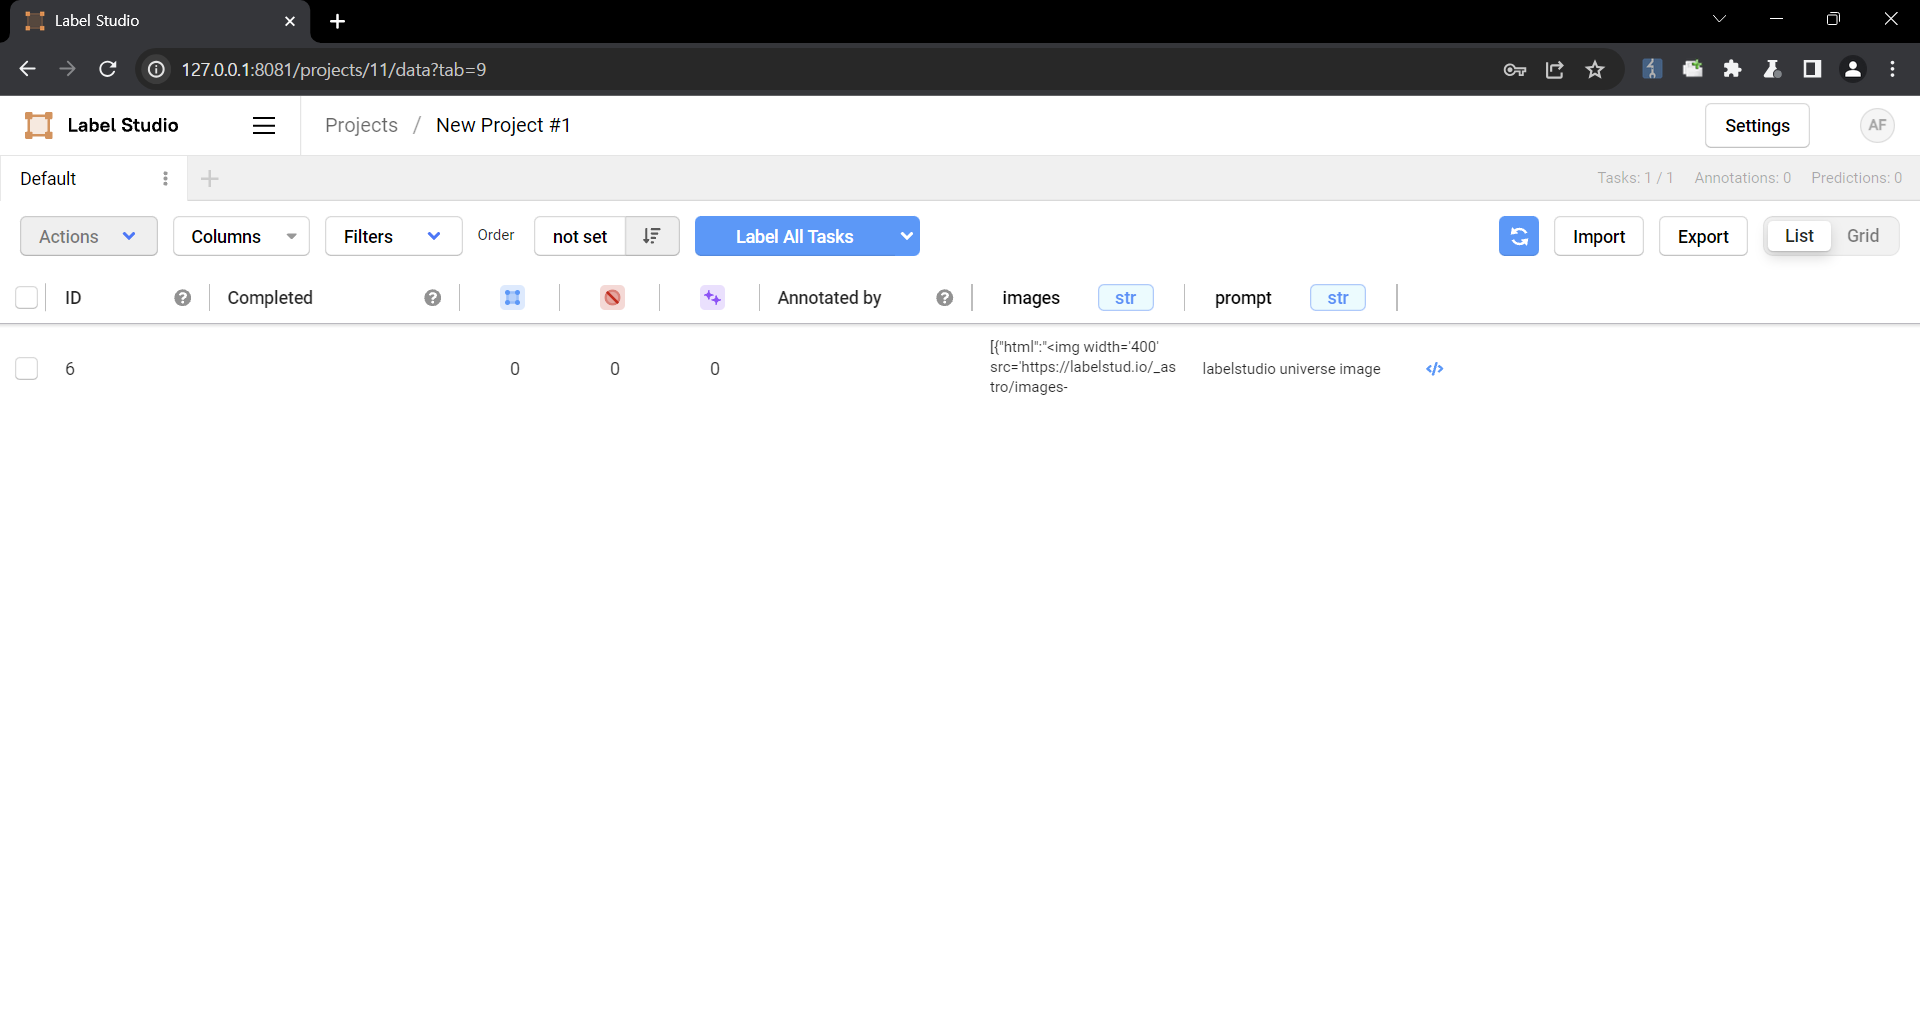
5. Check that the script is running 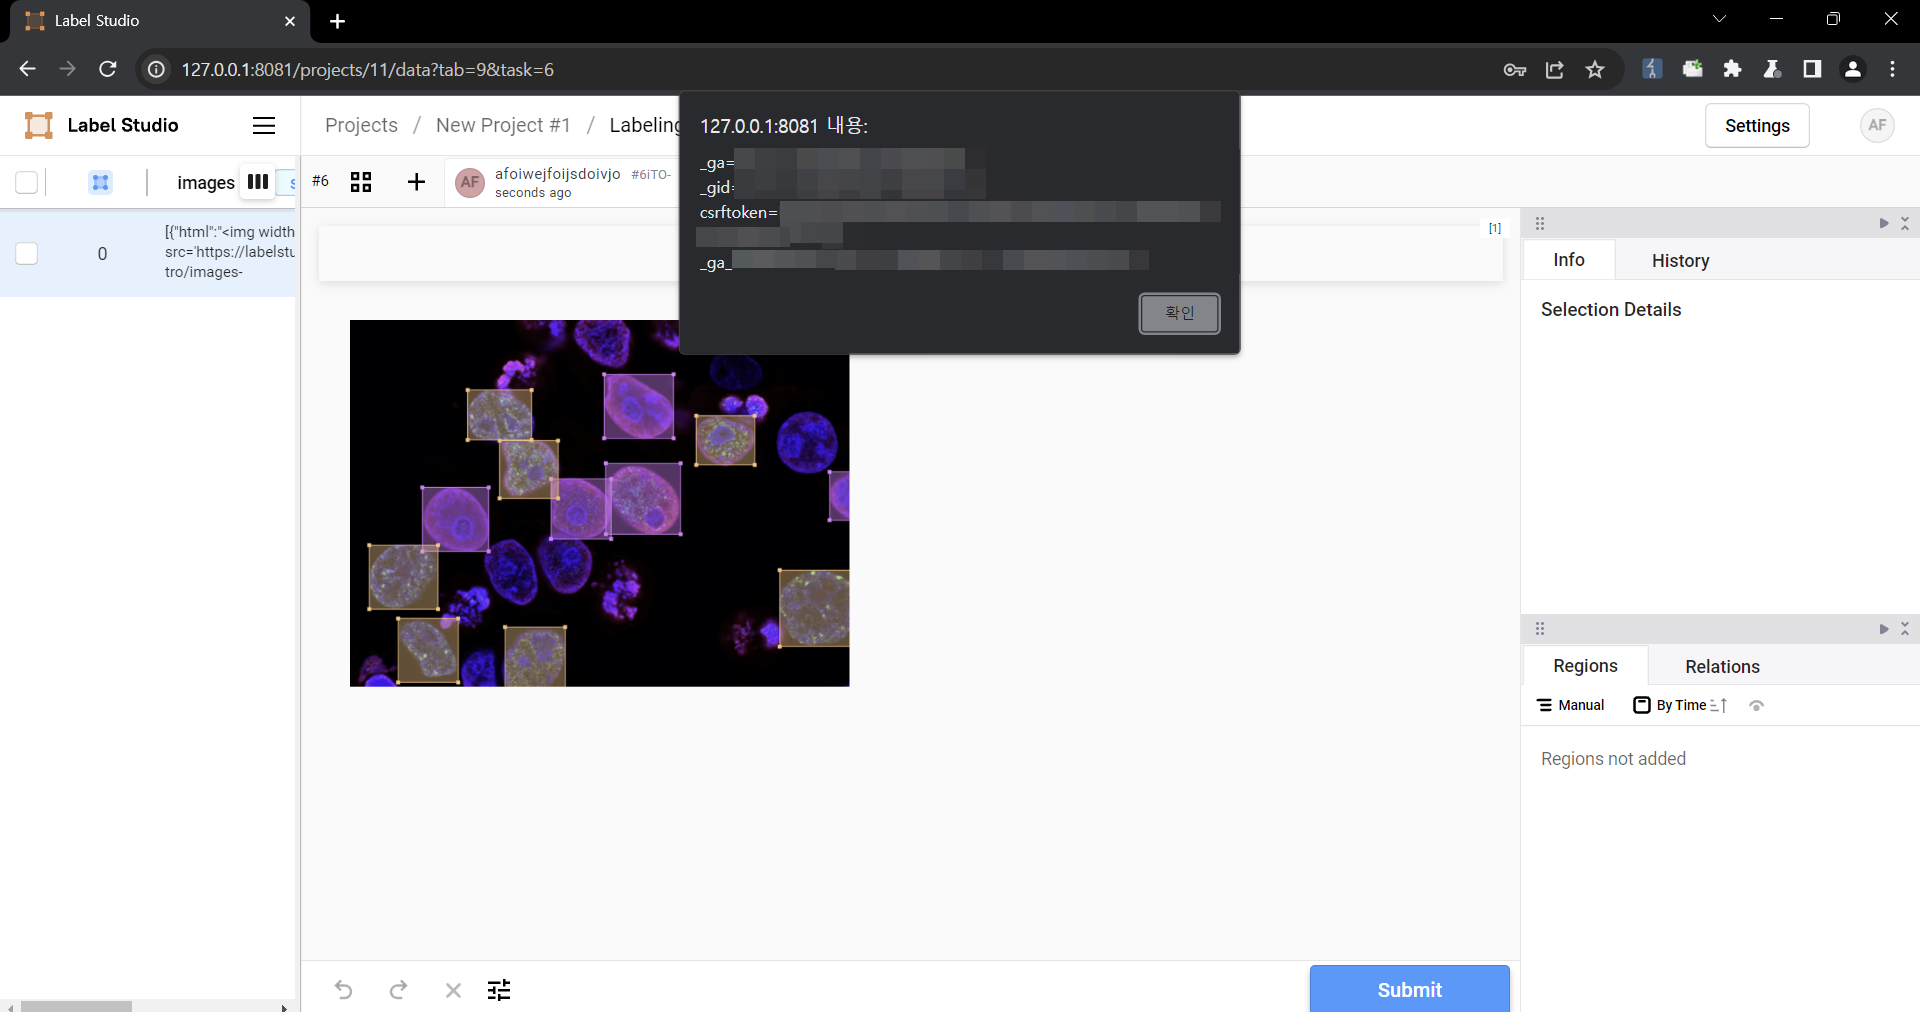
### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Weakness: CWE-79
Which versions are affected by CVE-2024-26152?
3 open source packages ship an affected version, including label-studio. It affects 1 product.
| Package | Affected | Fixed in |
|---|---|---|
label-studio PyPI | All versions | 1.11.0 |
label-studio PyPI | All versions | 1.11.0 |
label-studio PyPI | All versions | 1.11.0 |
Products include Humansignal Label Studio.
How do I fix CVE-2024-26152?
Upgrade label-studio to 1.11.0 or later.
Escape output for the context it lands in and set a strict Content Security Policy. Upgrading the affected component is the real fix. More about Cross-site scripting.
Is CVE-2024-26152 being exploited?
It is not confirmed as exploited in the wild, but public exploit code for CVE-2024-26152 exists.
Other vulnerabilities in HumanSignal label-studio
- CVE-2023-43791 Label Studio has Hardcoded Django `SECRET_KEY` that can be Abused to Forge Session Tokens
- CVE-2026-22033 Label Studio vulnerable to full account takeover by chaining Stored XSS + IDOR in User Profile via custom_hotkeys field
- CVE-2025-25297 Label Studio allows Server-Side Request Forgery in the S3 Storage Endpoint
- CVE-2025-47783 label-studio vulnerable to Cross-Site Scripting (Reflected) via the label_config parameter.
- CVE-2023-47117 Object Relational Mapper Leak Vulnerability in Filtering Task in Label Studio
Sources
Also known as GHSA-6xv9-957j-qfhg, PYSEC-2024-249.