
GHSA-fj52-5g4h-gmq8 pyLoad's Session Not Invalidated After Permission Changes
Attackers with valid sessions retain access to restricted data after permission revocation due to missing session invalidation in pyLoad.
- Exploited in the wild
- Not known
- Login needed
- Any signed-in user
- Attackable
- Over the internet
- Victim action needed
- Not needed
- Fix
- None listed
What is GHSA-fj52-5g4h-gmq8?
GHSA-fj52-5g4h-gmq8 is a missing authorization vulnerability in pyload-ng, published on 14 Apr 2026. Any signed-in user can exploit it over the network, with no action from the victim.
Official description
Summary
The pyload application does not properly invalidate or modify sessions upon changes made to a user's permissions.
Details
Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the pyload application, as a user with a valid session can still perform the actions.
PoC
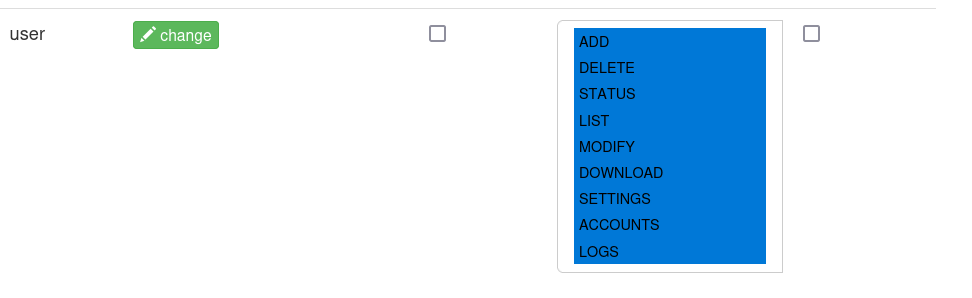
Take a user with all the permissions, as shown below.
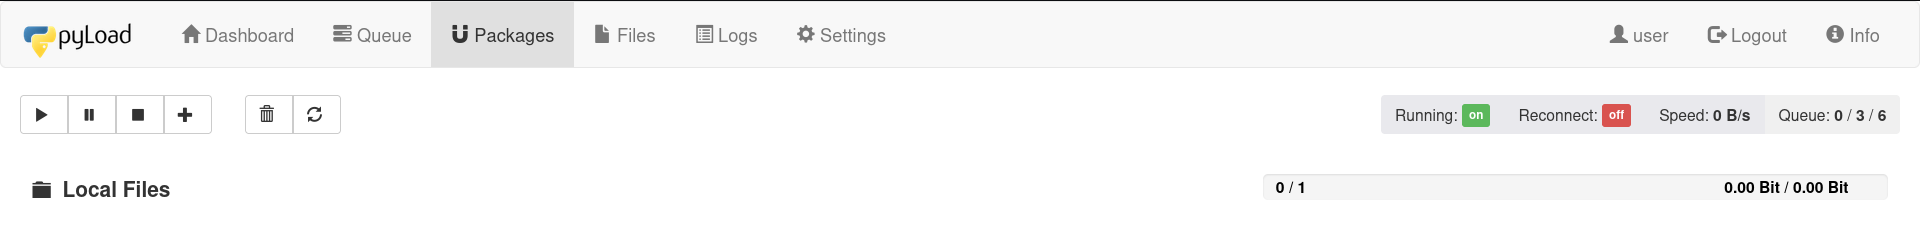
We now log in as this user.
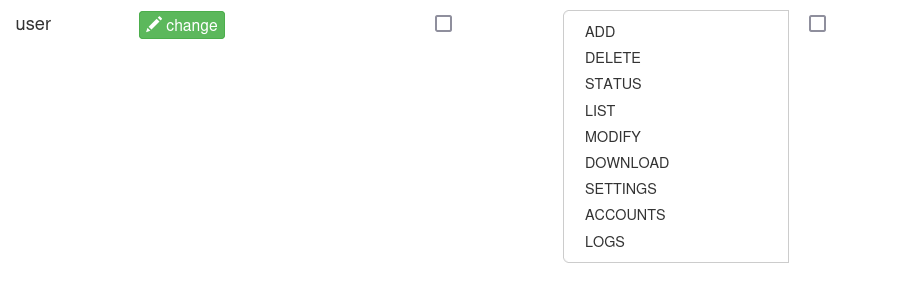
Let us now take away all the permissions.
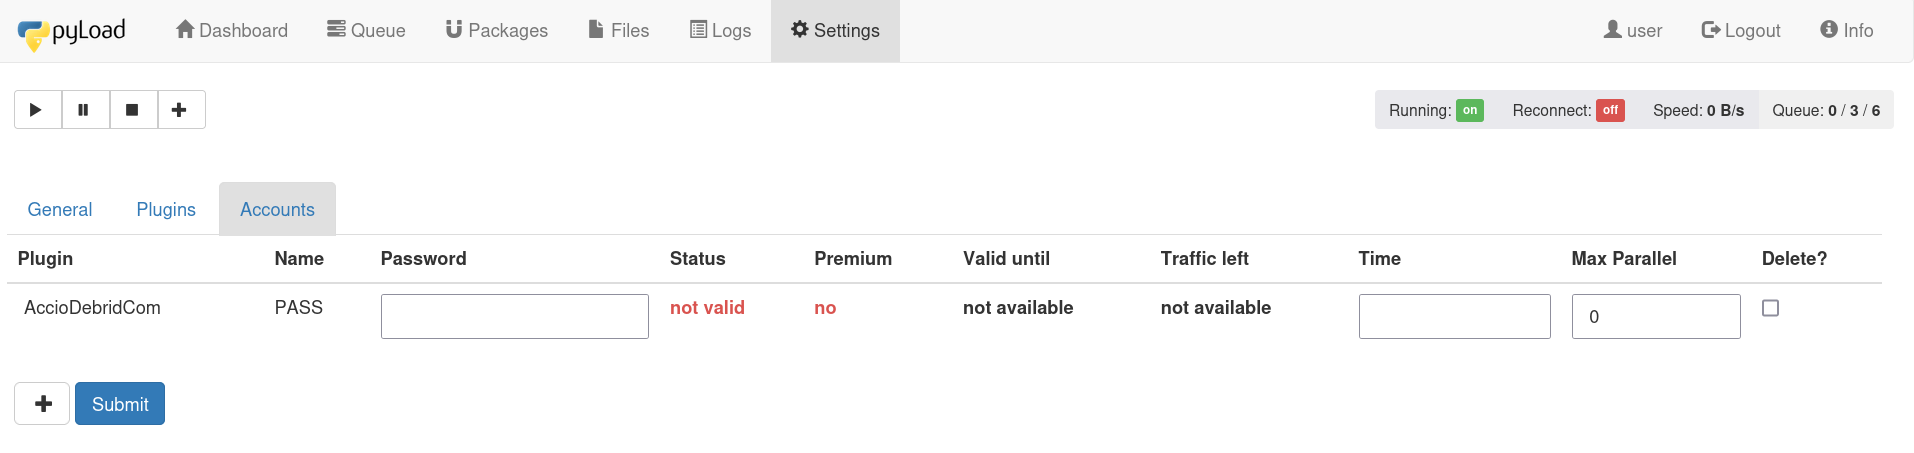
The logged in session can still be used to access everything in the application.
Impact
Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
Which versions are affected by GHSA-fj52-5g4h-gmq8?
2 open source packages ship an affected version, including pyload-ng.
| Package | Affected | Fixed in |
|---|---|---|
pyload-ng PyPI | All versions to 0.5.0b3.dev97 | None |
pyload-ng PyPI | All versions to 0.5.0b3.dev97 | None |
How do I fix GHSA-fj52-5g4h-gmq8?
No fix has been published for GHSA-fj52-5g4h-gmq8 yet. Limit exposure of the affected software until one is available.
Upgrade, and check permissions on every request on the server, not only in the interface. More about Missing authorization.
Is GHSA-fj52-5g4h-gmq8 being exploited?
There is no known exploitation of GHSA-fj52-5g4h-gmq8 in the wild and no public exploit code.