# GHSA-h29g-c9cx-c73q: torrentpier has PHP Serialize Injections
> Attackers can exploit PHP serialization flaws in Torrentpier to execute arbitrary code or read files on the server.
- **Severity:** Not scored
- **Exploited in the wild:** Not known
- **Login needed:** Not stated
- **Attackable:** Over the internet
- **Victim action needed:** Not stated
- **Fix available:** Yes
- **Published:** 11 May 2026
## What is GHSA-h29g-c9cx-c73q?
GHSA-h29g-c9cx-c73q is an unsafe deserialization vulnerability in torrentpier/torrentpier, published on 11 May 2026. It can be exploited over the network.
### Official description
### Summary
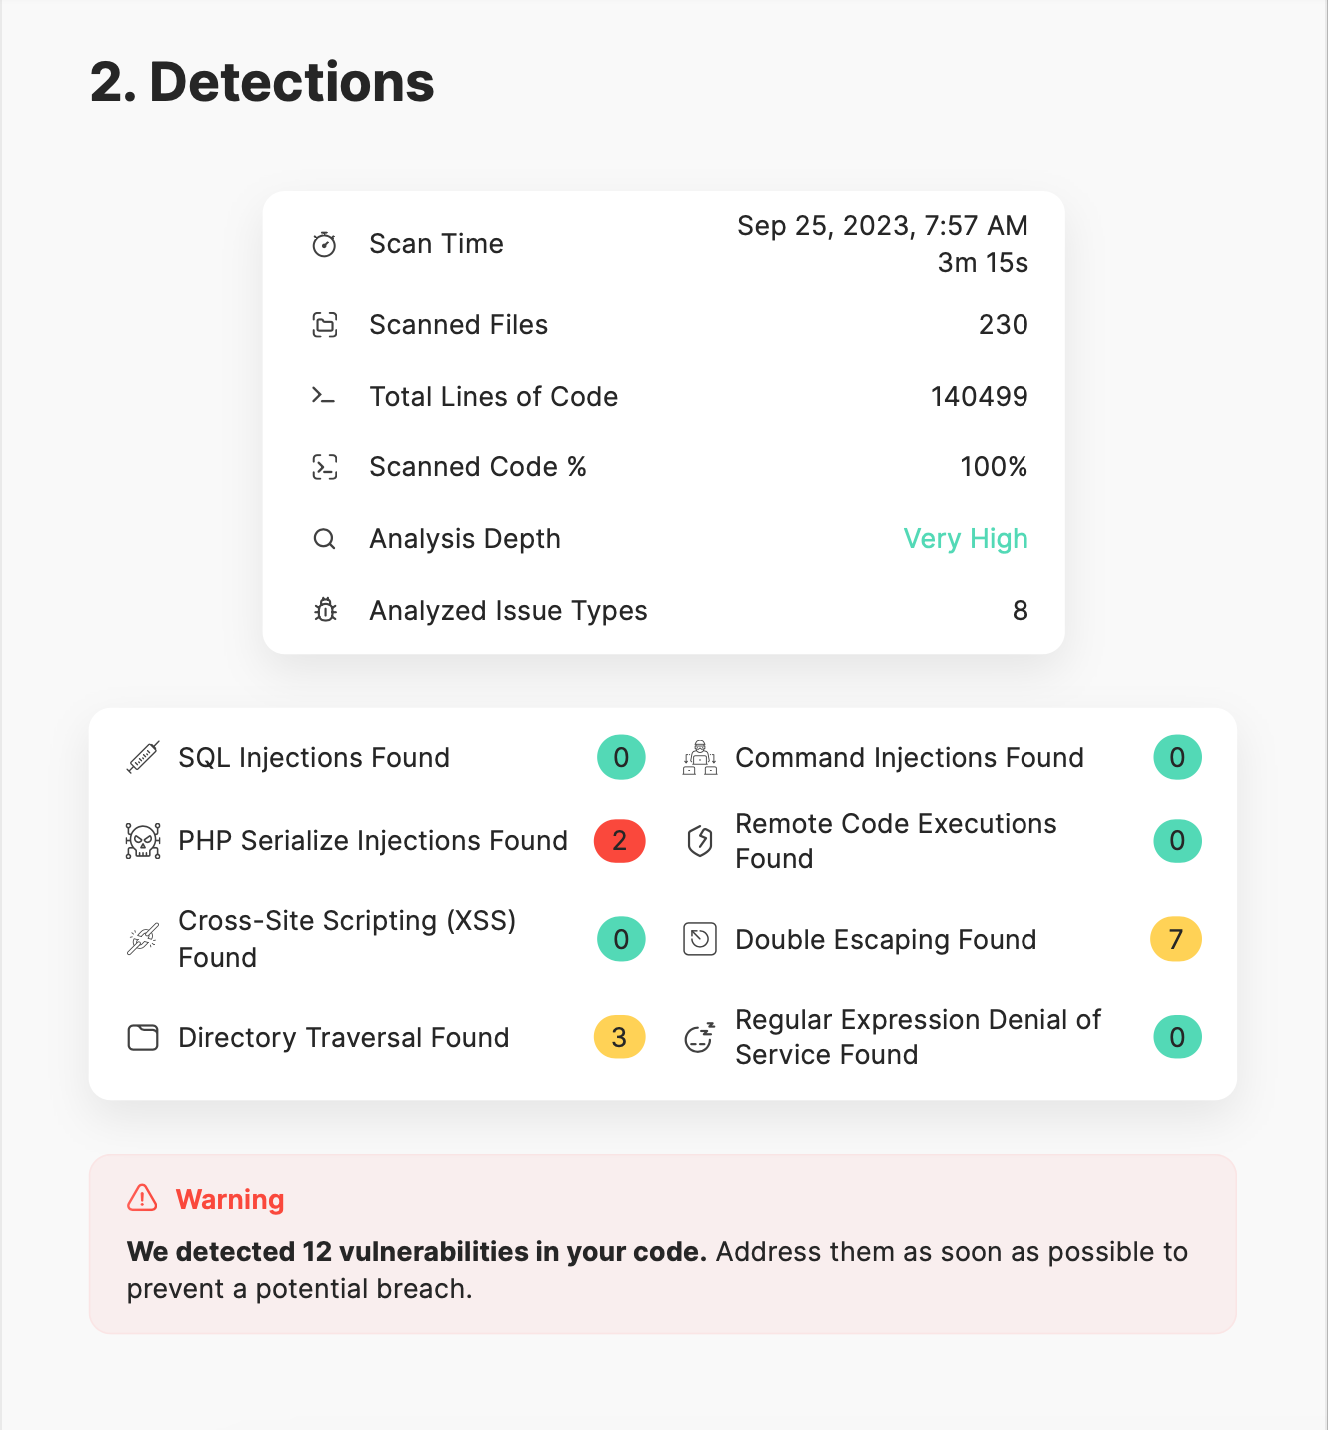
Hi, there. We've found PHP Serialize Injections in your project “torrentpier". According to the OWASP, it can pose a significant risk: enable an attacker to modify serialized objects in order to inject malicious data into the application code, resulting in code execution or an arbitrary reading of the file on any vulnerable system.
### Details
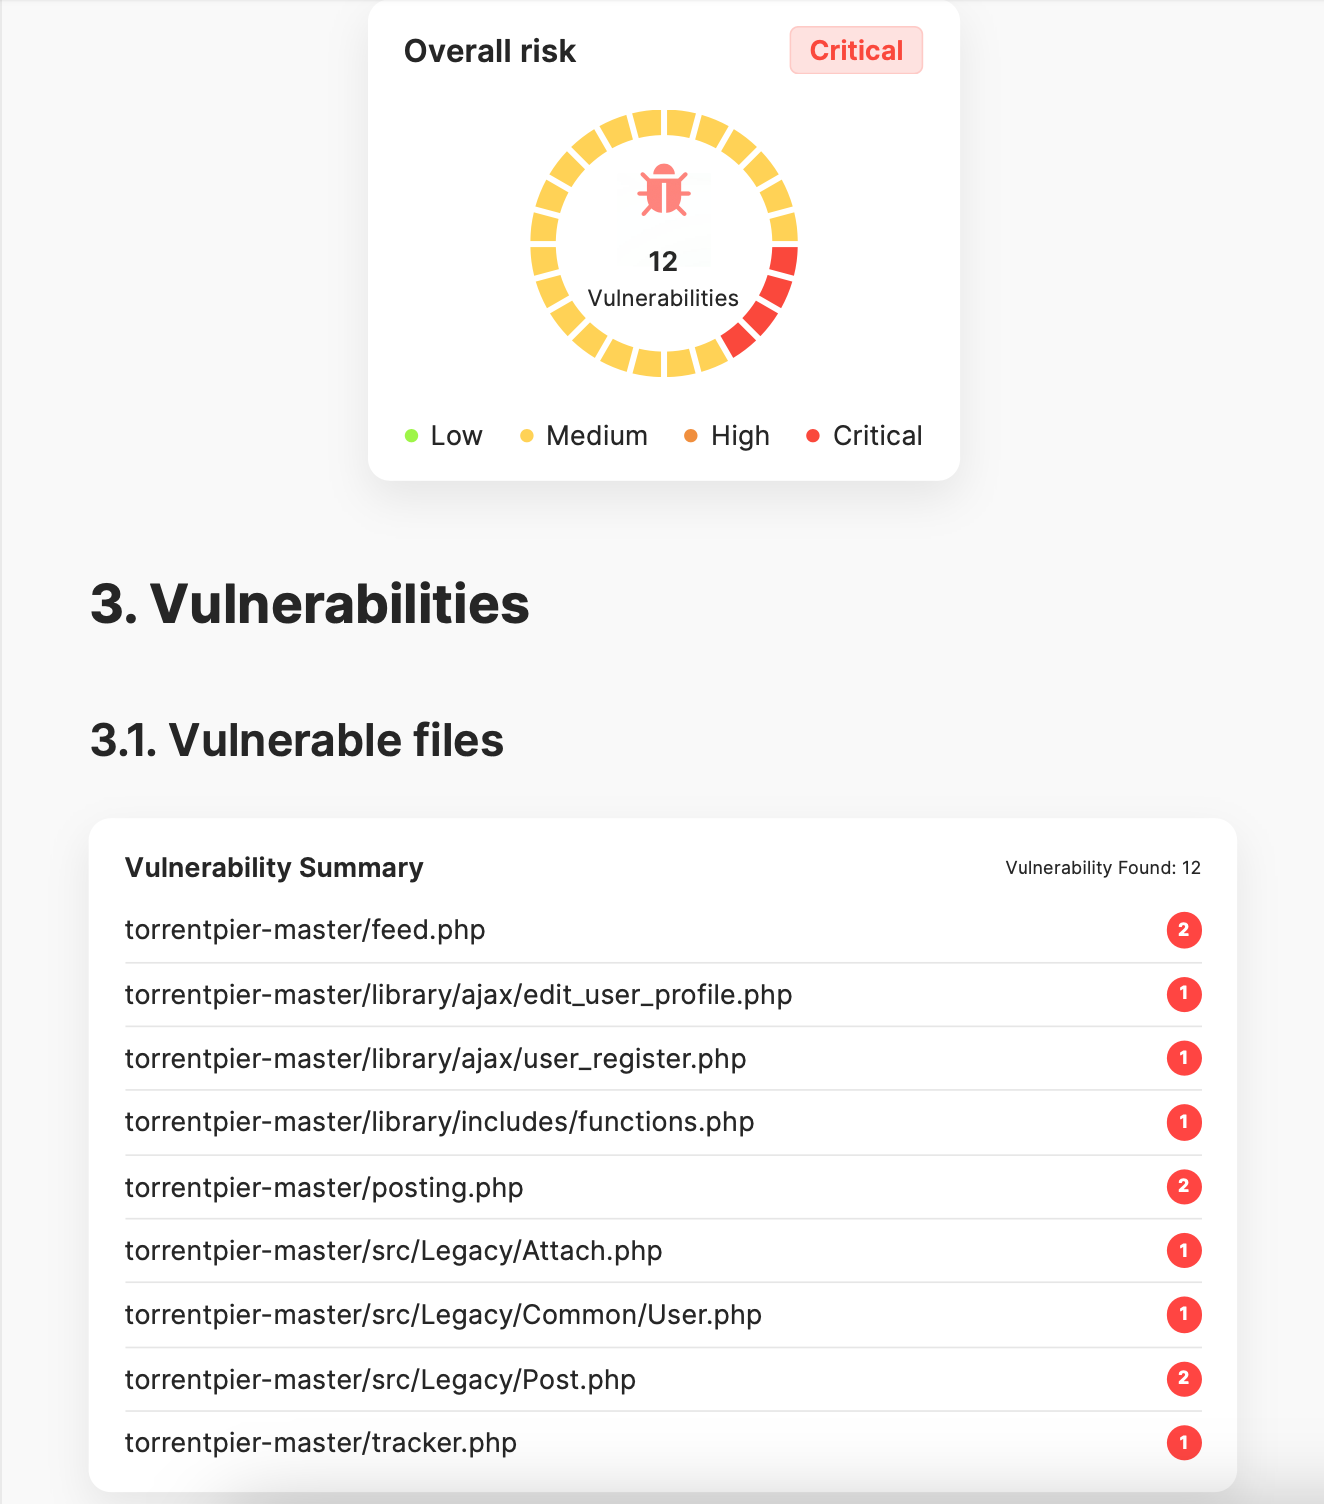
In the attachment you can find a report with the number of vulnerabilities, their types and the vulnerable files. To view the lines of vulnerable code you may scan your project with the "[PHP Secure](https://phpsecure.net/?utm_source=github&utm_term=torrentpier&utm_content=torrentpier)" vulnerability scanner with a full access to it.
### PoC
 ### About Us
We are a team of developers of the PHP Secure vulnerability scanner. First, we checked your code automatically. Then we reviewed the vulnerable code more deeply manually and felt it was necessary to report about it to you. We suggest you scanning your code and address vulnerabilities as soon as possible to prevent a potential breach.
If you have any questions, email us at support@phpsecure.net"
## Which versions are affected by GHSA-h29g-c9cx-c73q?
2 open source packages ship an affected version, including torrentpier/torrentpier.
| Package | Ecosystem | Affected | Fixed in |
| --- | --- | --- | --- |
| `torrentpier/torrentpier` | Packagist | All versions | 2.4.4 |
| `torrentpier/torrentpier` | Packagist | All versions | 2.4.4 |
## How do I fix GHSA-h29g-c9cx-c73q?
Upgrade torrentpier/torrentpier to 2.4.4 or later.
## Is GHSA-h29g-c9cx-c73q being exploited?
There is no known exploitation of GHSA-h29g-c9cx-c73q in the wild and no public exploit code.
## Fix prompt for AI coding agents
```text
Check this codebase for GHSA-h29g-c9cx-c73q and fix it if it is affected.
What it is: GHSA-h29g-c9cx-c73q is an unsafe deserialization vulnerability in torrentpier/torrentpier, published on 11 May 2026. It can be exploited over the network.
Exploitation: There is no known exploitation of GHSA-h29g-c9cx-c73q in the wild and no public exploit code.
Affected packages and fixed versions:
- torrentpier/torrentpier (Packagist): affected all versions; fixed in 2.4.4
- torrentpier/torrentpier (Packagist): affected all versions; fixed in 2.4.4
Task:
1. Search the dependency manifests and lockfiles (for example package.json, package-lock.json, requirements.txt, poetry.lock, uv.lock, pom.xml, build.gradle, go.mod, Cargo.lock, Gemfile.lock) and any Dockerfiles for the affected packages, including transitive dependencies.
2. If an affected version is in use, upgrade it to the fixed version for its release line with the project's package manager, so the lockfile is regenerated. Prefer the smallest upgrade that fixes it.
3. If there is no fix, or the upgrade would break the build, do not guess: explain the risk and the safest workaround instead.
4. Run the tests and summarise what changed and why.
5. If nothing in the project is affected, say so and change nothing.
Reference: https://insights.sbomify.com/GHSA-h29g-c9cx-c73q/ (Markdown: https://insights.sbomify.com/GHSA-h29g-c9cx-c73q/index.md)
```
## Sources
- OSV: https://osv.dev/vulnerability/GHSA-h29g-c9cx-c73q
---
From sbomify Insights: https://insights.sbomify.com/GHSA-h29g-c9cx-c73q/
Summaries are generated and may contain mistakes; the official description above is the record.